

SentryBERT Threat Radar Pro

Overview
On-device security stream intelligence running local INT8 neural inference passes.
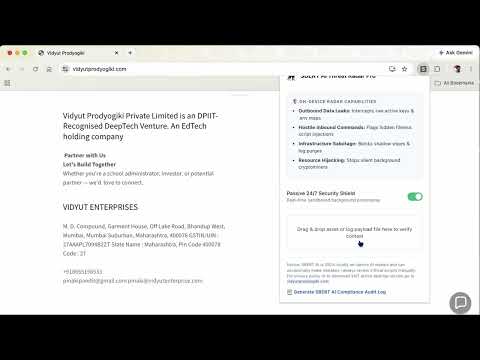
🎯 SBERT AI Advanced Threat Radar Pro: Enterprise-Grade Viewport Infrastructure Protection & Zero-Egress On-Device Stream Auditing SentryBERT Threat Radar Pro introduces a localized architectural layer designed to bring real-time, zero-latency security intelligence straight into your browser's viewport context. Engineered specifically for security engineers, system administrators, cloud architects, and compliance officers, this extension serves as a sandboxed, client-side shield against data leaks, hostile command scripts, and infrastructure manipulation vectors. By executing pure, deterministic local text-matrix vector analysis directly inside an isolated browser process, SentryBERT scans your code blocks, terminal logs, environment files, and infrastructure matrices with absolute privacy. No tracking scripts, no phone-home servers, no external cloud dependencies—Zero Cloud Data Egress. 100% On-Device Isolation. 🎯 CORE SECURITY SCANNING VECTOR MODULES The application functions as a local deep-inspection gateway, utilizing tokenized input vector spaces to instantly intercept, isolate, and flag hidden risk patterns across four core critical categories before they escape your local host environment: 1️⃣ Outbound Data Leak Prevention & Cryptographic Exfiltration Shield Accidental data exposure through copying, pasting, or dragging files into web forms is one of the leading causes of enterprise cloud breaches. SentryBERT continuously monitors its sandboxed container zone to capture accidental leaks of private cryptographic assets (such as id_rsa or raw SSH keys), raw database connection strings (DATABASE_URL), cloud deployment configuration arrays (.env files), infrastructure-as-code (IaC) blueprints (Terraform, Ansible), and active third-party developer API tokens. It intercepts the payload and sounds an immediate visual alarm, blocking exposure before data transits external network boundaries. 2️⃣ Hostile Inbound Interception & Reverse-Shell Analysis Engine Attackers frequently embed malicious execution strings into server scripts or document packages. SentryBERT evaluates inbound data streams to catch fileless, memory-only stagers, unauthorized shell spawning sequences, or interactive reverse-backdoors hidden behind standard communication protocols (such as bash -i >& /dev/tcp/, raw Netcat listener invocations nc -e /bin/sh, or advanced PowerShell download strings). The engine identifies these malicious character layouts even if they are obfuscated within deep configuration code, giving you immediate local visibility into system attack attempts. 3️⃣ Infrastructure Sabotage Shield & Log-Clearing Defense Protect your system environment against administrative tampering and destructive scripts. SentryBERT flags malicious strings designed to silently erase local shadow copies (vssadmin delete shadows), wipe critical system logging histories (wevtutil cl), stop essential security daemons, or execute destructive directory commands (rm -rf /). This layer acts as a local security check, verifying that configuration updates or code dependencies don't hide destructive code meant to blind or disable your system. 4️⃣ Resource Hijacking Prevention & Cryptojacking Guard Malicious cryptocurrency miners can silently degrade device computing performance and drive up host infrastructure costs. SentryBERT maps the structural layout configurations of crypto-jacking stagers (such as Stratum mining protocols and embedded config.json miner parameters) before they can anchor themselves into background execution environments, keeping your browser tabs fast and your local processor cool. ⚡ TECHNICAL HIGH-PERFORMANCE ENGINE & PRIVILEGE ISOLATION PROTOCOLS • Micro-Footprint WebAssembly Execution: SentryBERT is compiled as a high-efficiency text-matrix tokenizer with an uncompressed code bundle under 1MB. By leveraging highly optimized vector loops, it processes massive script documents in under 35 milliseconds per window without causing memory drops, lagging your layout canvas, or draining device battery life. • Quarantined Offscreen Document Sandbox: Security processing must never risk page layout stability. SentryBERT executes all tokenization matrices and linear evaluation blocks within a completely isolated, background Chrome Offscreen document (offscreen.html). This structure establishes a strict browser sandbox barrier, ensuring that text analysis cannot impact or be modified by active webpage runtimes. • Verified Minimalist Permissions Model: In alignment with Google's Principle of Least Privilege, SentryBERT requires only two core browser hooks to function: storage and offscreen. It possesses no host permissions, cannot read your history, cannot inject code across external domains, cannot touch browser cookies, and lacks the network privileges required to transmit data anywhere outside your machine. ⚠️ SYSTEM COMPLIANCE NOTICE & OPEN-SOURCE PEER GROUNDING Notice: Extension environment constraints limit on-device parameter size. Models can occasionally make mistakes. For our privacy policy or to download our more capable enterprise desktop versions, visit vidyutprodyogiki.com. SentryBERT Threat Radar Pro is designed to function as an immediate, on-device safety verification layer. Because adversarial threat patterns and tax compliance regulations change rapidly across global spaces, edge verification tools should be used as a helpful real-time warning tracker—always verify enterprise script deployments manually. To maintain absolute professional transparency and trust within the developer community, the extension's entire source code, processing layers, and manifest structures are completely open for public security peer review.
0 out of 5No ratings
Details
- Version1.0.3
- UpdatedOctober 27, 2026
- Offered byVidyut Prodyogiki
- Size2.21MiB
- LanguagesEnglish
- DeveloperVidyut Prodyogiki Pvt. Ltd.
Om Manusmruti Hsg Society, Dongri Pada, GB road. B-504 Thane, Maharashtra 400615 INEmail
pinakipandit@gmail.comPhone
+91 98922 38533 - TraderThis developer has identified itself as a trader per the definition from the European Union and committed to only offer products or services that comply with EU laws.
Privacy
This developer declares that your data is
- Not being sold to third parties, outside of the approved use cases
- Not being used or transferred for purposes that are unrelated to the item's core functionality
- Not being used or transferred to determine creditworthiness or for lending purposes
Support
For help with questions, suggestions, or problems, please open this page on your desktop browser