

AuthTailor

Overview
SAML & OIDC tracer: record a login live, decode JWTs and SAML responses, find what breaks single sign-on – locally in the browser.
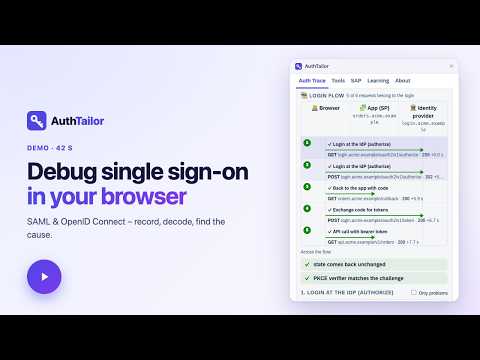
AuthTailor shows you what really happens when a single sign-on login runs, and why it fails. RECORD LIVE Press "Record live" and sign in to any app in any tab. AuthTailor draws the flow Browser → App → Identity provider as a sequence diagram and checks every step: state, nonce, PKCE, redirect_uri, InResponseTo, ACS URL and RelayState, across the whole flow. PASTE ANYTHING Paste or drop a SAML Response, AuthnRequest, Assertion or metadata (XML, Base64 or redirect-deflate), a JWT, a login URL, a token request or response, a discovery document, JWKS, a HAR file, or simply the error message – known error codes are explained with cause and fix. SEE THE TOKEN - JWTs taken apart into header, payload and signature. - Chain of trust from issuer to signature to audience. - An ID card with name, scopes and roles. - Times shown relative to now, with clock-skew tolerance. SAML, VISUAL Building blocks nested as in the XML, with signature seals and colour-coded findings. HEADERS, MASKED Request and response headers for every step, with a SameSite check of the cookies on the cross-site POST back to the app. Cookie values, Authorization, CSRF tokens and API keys are masked as they are recorded. BEARER TOKENS (OPTIONAL) See the JWTs that a single-page app sends to its API, including the rejection reason from WWW-Authenticate – and DPoP proofs checked against the request and the token binding. SIGNATURES, REALLY CHECKED SAML signatures are verified cryptographically with the certificate and compared with the fingerprint from your IdP metadata. JWTs are verified with the issuer's public keys, fetched on your click. Expiring certificates and missing keys after a rollover are flagged. SECURITY RATING A traffic light per area – flow & protocol, tokens & signatures, transport & leaks, cookies & session, browser protection. It finds signature wrapping, comments in the NameID, DTDs, jku/x5u in JWT headers, codes leaking via the Referer, tokens in URLs, client secrets sent from the browser, missing HSTS or frame protection, weak cookies, refresh tokens that are not rotated, and logouts that leave the session alive. TOOLS - Passkeys: decode a WebAuthn response – flags, authenticator, origin, RP ID and challenge checked. - Certificates and keys: PEM chains, CSRs, public and private keys, JWKs – order, expiry, key size, SHA-1, host name, whether key and certificate belong together. - Web security: rate a Content Security Policy (with a stricter suggestion), the security headers of a login page and a CORS preflight; spot look-alike and punycode login links and open redirects. - Secret scanner for any text, and a HAR cleaner that masks cookies, tokens, codes and passwords before you share a recording with support. - Page storage: on your click, find tokens in localStorage, sessionStorage and IndexedDB of the current tab – only type and length come back, never a value. SAP XSUAA and IAS tokens explained, "Why 403?" scope by scope, reviews of xs-security.json, xs-app.json, service keys and destinations, logon tickets (MYSAPSSO2) with signature check, BTP flows such as principal propagation as diagrams, and SAP Gateway and ICF errors with cause and fix. LEARNING Basics in eight short chapters, a glossary, known error messages with cause and fix, a go-live checklist – and 13 flows of OAuth 2.0, OpenID Connect and SAML as step-by-step sequence diagrams, with what to watch and what AuthTailor checks. MARKDOWN REPORT Verdict, rating, flows, findings and steps, ready for a ticket – masked. PRIVATE BY DESIGN - Runs entirely in the browser: no server, no account, no tracking. - Recordings stay in memory only while the panel is open. - Host access is requested only when you start recording (or allow a page scan) and is given back right after. Made by CloudDNA, SAP partner from Austria – https://www.clouddna.at/
0 out of 5No ratings
Details
- Version1.0.0
- UpdatedNovember 8, 2026
- Offered byCloudDNA GmbH
- Size211KiB
- Languages2 languages
- DeveloperCloudDNA GmbH
Untere Hauptstraße 23 Loipersdorf im Burgenland 7410 ATEmail
office@clouddna.atPhone
+43 664 1964199 - TraderThis developer has identified itself as a trader per the definition from the European Union and committed to only offer products or services that comply with EU laws.
- D-U-N-S300540079
Privacy

AuthTailor has disclosed the following information regarding the collection and usage of your data. More detailed information can be found in the developer's privacy policy.
AuthTailor handles the following:
This developer declares that your data is
- Not being sold to third parties, outside of the approved use cases
- Not being used or transferred for purposes that are unrelated to the item's core functionality
- Not being used or transferred to determine creditworthiness or for lending purposes