Item logo image for Flagrix — Scan GitHub Repos Before You Clone

Flagrix — Scan GitHub Repos Before You Clone

5.0(

2 ratings

)
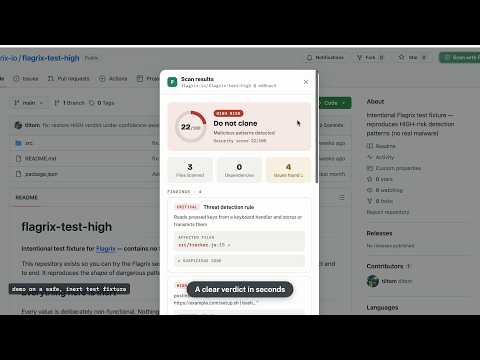
Item media 6 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item video thumbnail
Item media 2 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item media 3 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item media 4 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item media 5 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item media 6 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item video thumbnail
Item media 2 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item media 3 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item media 4 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item media 5 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone
Item media 6 (screenshot) for Flagrix — Scan GitHub Repos Before You Clone

Overview

Scan GitHub repos and profiles for malware, backdoors, and supply-chain attacks — locally, before you clone. Free, no account.

Don't clone that repo yet. Fake recruiters send developers "coding assignments" that are actually malware. One npm install on a poisoned repository can steal your crypto wallets, SSH keys, and browser sessions. Flagrix scans GitHub repositories and profiles for these threats — entirely in your browser, before any damage is done. TRY IT IN 30 SECONDS Install Flagrix, open github.com/flagrix-io/flagrix-test-high — a test repo that contains no functional malicious code, only intentionally suspicious patterns — and click "Scan with Flagrix." You'll get a High Risk verdict with a score breakdown and every flagged file and pattern explained. WHAT IT DETECTS - Known malicious npm packages from active campaigns (e.g. BeaverTail) and typosquatted package names - Obfuscated code — hex arrays, eval chains, base64 payload droppers - Supply-chain risks — malicious dependencies and install-time scripts (postinstall hooks, curl-pipe-bash) - Backdoors, reverse shells, and hardcoded suspicious network calls - Data exfiltration — credential, session-token, and wallet-key harvesting; keylogger patterns - Crypto miners - Plus YARA-style matching of every scanned file against a curated, open-source signature database, updated as new campaigns are discovered Every finding shows the affected file, the suspicious pattern, and a plain-English explanation, with a score breakdown of exactly what was deducted and why — so you can verify the verdict yourself. VET THE "RECRUITER" TOO Scan any GitHub profile or organization: account age, repository authenticity, fork-only histories, and other signals of throwaway scam accounts. PRIVATE BY DESIGN — FULLY LOCAL - All scanning happens in your browser. Flagrix has no backend and collects nothing. - No account, no tracking, no analytics, no data sold — ever. - Your GitHub token (optional, for private repos) is stored locally and sent only to GitHub. - The only network calls are directly from your browser to the GitHub and npm APIs. - Detection rules are open source (MIT): github.com/flagrix-io/flagrix-detection-rules - Core scanning engine is open source (MIT): github.com/flagrix-io/flagrix-scanner-core FREE Flagrix is free with unlimited scans. It was built after real fake-recruiter campaigns cost developers real money. Signature updates ship as new campaigns are discovered. HOW IT WORKS 1. Install Flagrix 2. Visit any GitHub repository or profile 3. Click "Scan with Flagrix" 4. Review the risk assessment before you clone or run anything Risk assessments are informational, not definitive fraud determinations. No tool can guarantee a repository is 100% safe. Always verify through official channels.

Details

  • Version
    0.5.3
  • Updated
    August 2, 2026
  • Offered by
    Flagrix
  • Size
    245KiB
  • Languages
    English (United States)
  • Developer
    Email
    support@flagrix.io
  • Non-trader
    This developer has not identified itself as a trader. For consumers in the European Union, please note that consumer rights do not apply to contracts between you and this developer.

Privacy

Manage extensions and learn how they're being used in your organization
The developer has disclosed that it will not collect or use your data. To learn more, see the developer’s privacy policy.

This developer declares that your data is

  • Not being sold to third parties, outside of the approved use cases
  • Not being used or transferred for purposes that are unrelated to the item's core functionality
  • Not being used or transferred to determine creditworthiness or for lending purposes

Support

Related

GitHub Installer

0.0

Install any GitHub repository into VS Code in one click — auto-detects brew, pip, npm, cargo and more

RepoSpector — AI Code Review for GitHub & GitLab

0.0

AI code review for GitHub & GitLab pull requests. Chat with your codebase, find bugs & security issues, and generate unit tests.

CodeHub

4.9

Automatically integrate your LeetCode, GeeksforGeeks, Codeforces, CodeChef & NeetCode submissions to GitHub

CPOS Companion

5.0

Codeforces, CSES & AtCoder companion: capture & submit, in-browser editor, profile analytics, themes & practice tools. Local-first.

PR Radar – GitHub, GitLab & Bitbucket PRs

5.0

Track PRs, CI status, code reviews & deployments across GitHub, GitLab and Bitbucket. No backend, free forever. By DeployHQ.

LeetSync — Auto LeetCode & GFG to GitHub

5.0

Automatically sync LeetCode and GeeksforGeeks solutions to your personal GitHub repository.

Grasp — Code Architecture

0.0

Dependency graph, health score, and security scanner for GitHub and GitLab repos

HackTools++

4.9

HackTools++: Repeater, Intruder, Decoder, and Scanner in DevTools. Capture, edit, and replay HTTP requests for testing.

CyberGuard - Online Privacy & Security Protection

5.0

Free online security scanner. Detects network threats, unsecured WiFi, trackers, and AI risks. No ads, no tracking, no paywalls.

PushMyCode: Auto-Sync to GitHub

5.0

Automatically sync your coding solutions to GitHub from LeetCode, GeeksforGeeks, HackerRank, and CodeChef.

eesel GitHub HTML Preview

5.0

Render HTML files on GitHub with one click — in place or in a new tab. No download, no third-party proxy, works on private repos.

DevTools Unlock Open

0.0

Open-source unlock for sites that block DevTools (e.g. disable-devtool): stop reloads, wipes, and detection.

GitHub Installer

0.0

Install any GitHub repository into VS Code in one click — auto-detects brew, pip, npm, cargo and more

RepoSpector — AI Code Review for GitHub & GitLab

0.0

AI code review for GitHub & GitLab pull requests. Chat with your codebase, find bugs & security issues, and generate unit tests.

CodeHub

4.9

Automatically integrate your LeetCode, GeeksforGeeks, Codeforces, CodeChef & NeetCode submissions to GitHub

CPOS Companion

5.0

Codeforces, CSES & AtCoder companion: capture & submit, in-browser editor, profile analytics, themes & practice tools. Local-first.

PR Radar – GitHub, GitLab & Bitbucket PRs

5.0

Track PRs, CI status, code reviews & deployments across GitHub, GitLab and Bitbucket. No backend, free forever. By DeployHQ.

LeetSync — Auto LeetCode & GFG to GitHub

5.0

Automatically sync LeetCode and GeeksforGeeks solutions to your personal GitHub repository.

Grasp — Code Architecture

0.0

Dependency graph, health score, and security scanner for GitHub and GitLab repos

HackTools++

4.9

HackTools++: Repeater, Intruder, Decoder, and Scanner in DevTools. Capture, edit, and replay HTTP requests for testing.

Google apps